FBI Cybersecurity Executive Arrested in Major Escalation of ShinyHunters Investigation
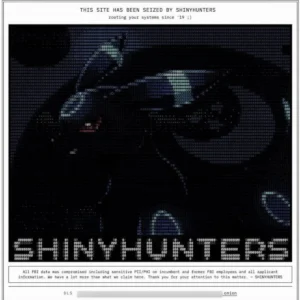
In a stunning turn of events that has sent shockwaves through the cybersecurity and cyber-insurance industries, federal authorities have apprehended a prominent executive at a Canadian cybersecurity firm in connection with the sprawling investigation into the notorious hacking collective known as "ShinyHunters." The arrest, which took place in Pennsylvania this week, marks a significant escalation in the FBI’s pursuit of a group that recently managed to breach the Bureau’s own internal systems, exfiltrating sensitive data regarding thousands of federal agents.
The suspect, identified in federal court records as Edward Dubrovsky, was taken into custody on October 8. While the arrest was initially shrouded in mystery, multiple sources have confirmed that the investigation into ShinyHunters—a group known for high-stakes extortion and large-scale data theft—has been centralized within the Eastern District of Texas.
The Arrest and Legal Proceedings
The arrest occurred under dramatic circumstances: Dubrovsky was in Philadelphia attending the annual "Cyber Risk Summit," an industry-focused event held at the Loews Philadelphia Hotel between October 5 and October 7. Federal agents intercepted the executive, who has built a career advising companies on how to navigate the treacherous waters of ransomware negotiations.
Court documents filed in the Eastern District of Pennsylvania—and subsequently moved to the Eastern District of Texas—charge the defendant with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." While the primary complaint remains under seal, the charges reflect a grave assessment of the suspect’s alleged role in the criminal enterprise.
As of this writing, Dubrovsky is being held at a federal facility in Philadelphia. He has yet to be assigned a public defender, and his legal representation remains unclear. The FBI, for its part, has maintained a wall of silence, declining to comment on the specifics of the ongoing investigation.
Chronology: The Rise of the "ShinyHunters" and the Net Tightens
The arrest of Dubrovsky is the latest in a series of high-profile developments that have targeted the infrastructure of the ShinyHunters group. The timeline of this investigation reveals a calculated effort by federal authorities to dismantle the group from the inside out:

- Early 2026: ShinyHunters accelerates its operations, utilizing sophisticated phishing campaigns and credential theft to siphon data from SaaS (Software-as-a-Service) providers. The group gains notoriety for extorting over $70 million from corporate victims within the year.
- September 2026: Dutch authorities arrest Pepijn van der Stap, a convicted cybercriminal, on charges linked to the ShinyHunters operation. The FBI begins an exhaustive analysis of digital devices seized during the raid.
- Late September 2026: Following the arrest of Van der Stap, an operative known as "Rey" assumes leadership of the group. Emboldened, Rey begins taunting the FBI, publicly claiming to have stolen sensitive recruitment data, medical records, and psychiatric evaluations of federal agents.
- October 2026: Reuters reports that "Rey"—later identified as a teenager named Saif Al-din Khader—has been detained by authorities and is reportedly cooperating with investigators.
- October 5–7, 2026: The Cyber Risk Summit takes place in Philadelphia.
- October 8, 2026: Edward Dubrovsky is arrested by federal agents in Pennsylvania.
- October 9, 2026: The case is officially transferred to the Eastern District of Texas, signaling a centralized federal strategy against the group.
The Intersection of Security and Extortion
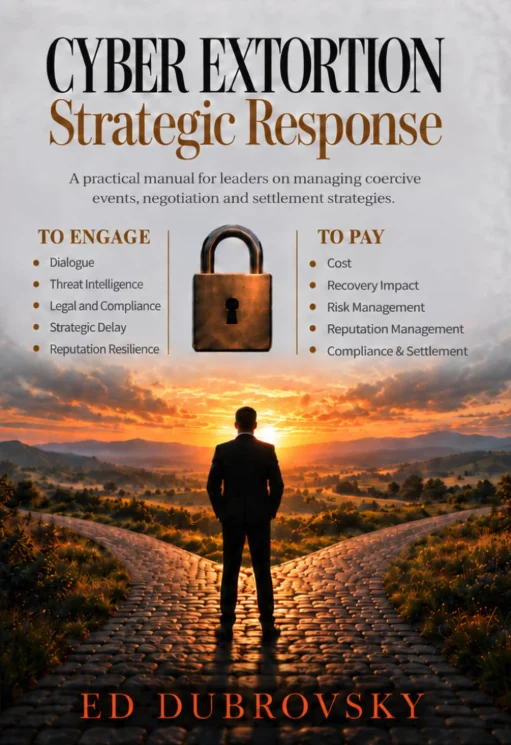
The arrest of a high-level security executive on charges of assisting an extortion ring raises uncomfortable questions about the "ransomware-as-a-service" ecosystem. Dubrovsky, a veteran in the field, is the author of the book Cyber Extortion Strategic Response, a manual that purports to guide organizations through the complexities of ransomware.
In his professional capacity, Dubrovsky argued that engagement with criminals was a necessary evil, stating that "communicating with a criminal is not the same as negotiating a payment." However, federal prosecutors now allege that the line between "advising" and "facilitating" was crossed.
The industry has been quick to distance itself from the fallout. Following the reports, a spokesperson for the security firm Cypfer issued a statement clarifying that while Dubrovsky was associated with the firm as a managing director, he was not a founder, as his LinkedIn profile had previously suggested. He resigned from the position in November 2025.
Implications for the Cybersecurity Industry
The involvement of a professional negotiator in a criminal conspiracy is a worst-case scenario for the cybersecurity sector. For years, companies have turned to specialized firms to handle ransom demands, hoping to mitigate data exposure and business interruption. If executives within these firms are found to be working in tandem with the threat actors they are supposed to be negotiating against, the entire model of cyber-insurance and professional incident response may face a regulatory reckoning.
Furthermore, the brazenness of ShinyHunters—specifically their decision to target the FBI’s own recruitment portal—suggests a shift in the threat landscape. By attacking the Bureau, the group signaled that no entity, regardless of its defensive capabilities, is immune. The theft of medical and psychiatric records of federal agents is particularly concerning, as it provides leverage that could potentially be used for espionage or further extortion against government employees.
Official Responses and Future Outlook
While FBI Director Kash Patel has acknowledged the arrest via social media, the Bureau has provided no further details. The move of the case to Texas is widely viewed by legal experts as a sign that the government is preparing for a "mega-trial," one that will likely attempt to map the entire hierarchy of the ShinyHunters organization.

Sources close to the investigation have hinted that more arrests are likely. Investigators are reportedly looking into other "principals" at firms specializing in ransomware negotiation, suggesting that the scope of the investigation is widening. The FBI’s focus on the digital artifacts seized during the Van der Stap arrest suggests that the agency now has a significant roadmap of the group’s inner communications and financial movements.
As the legal proceedings unfold in Texas, the cybersecurity community is left to grapple with a difficult reality: the intermediaries tasked with securing the digital world may be as vulnerable to corruption as the systems they protect. For the victims of ShinyHunters, the arrests offer a modicum of justice, but for the industry at large, the coming months will likely be defined by internal audits, increased scrutiny of "negotiation" practices, and a fundamental reassessment of how businesses respond to the modern threat of digital extortion.
This investigation remains fluid. As the court docket continues to update and the FBI moves to unseal documents, further revelations regarding the depth of the collaboration between security professionals and the ShinyHunters collective are expected to emerge.
Disclaimer: This report is based on information available as of October 10, 2026. Given the sensitivity of the ongoing federal investigation, further details regarding the evidence against the defendant and the extent of the FBI data breach may be released in upcoming court filings.