Critical PHP Security Vulnerabilities Exposed: What You Need to Know About the 2026 Server Flaws
Main Facts
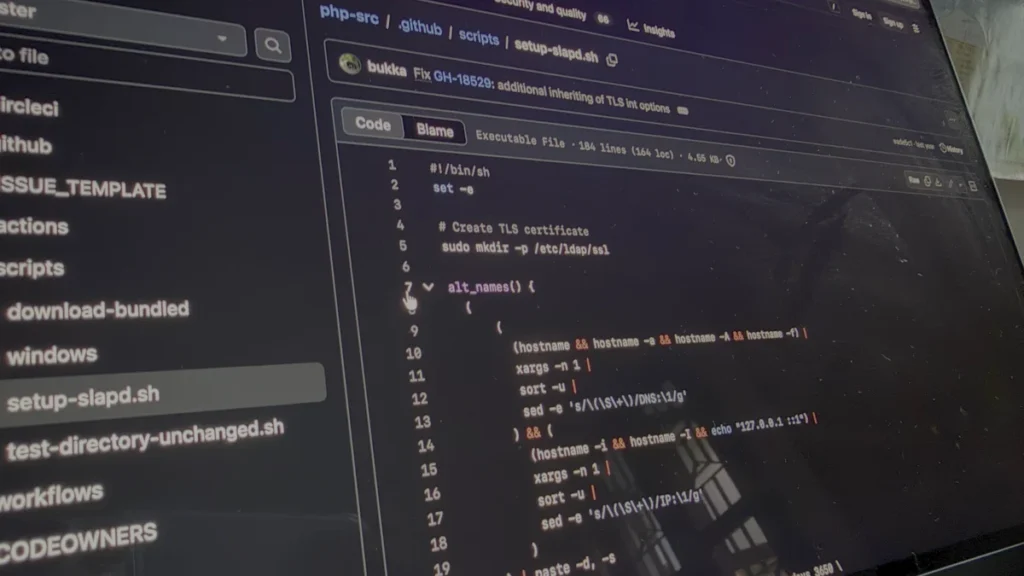
In late October 2026, the core development team behind PHP—one of the world’s most ubiquitous programming languages—disclosed two high-severity security vulnerabilities. These flaws potentially allow remote attackers to compromise web servers without needing physical access, valid user credentials, or prior authorization. Global cybersecurity agencies and independent researchers have issued widespread warnings, highlighting that successful exploitation could grant malicious actors full control over affected systems.
Because PHP operates quietly in the background of a vast majority of the internet, the discovery has sent ripples through the digital infrastructure landscape. PHP handles the server-side logic for millions of websites, ranging from small-scale blogs and independent online storefronts to massive enterprise networks, financial portals, and government databases.
The vulnerabilities stem from deep-seated memory management errors within the PHP engine itself:
- Memory Exhaustion Handling: When PHP runs critically low on available system memory, its error-handling routines occasionally mismanage half-finished data operations during the cleanup phase. This can result in severe memory corruption.
- Dangling Pointers ("Stale Notes"): Under specific error conditions, the PHP engine retains a reference (a pointer) to a memory address that has already been cleared or reallocated. When the system subsequently attempts to access what it believes is valid data, it interacts with unintended data, leading to further memory corruption.
A sophisticated attacker capable of triggering these memory corruption events can execute arbitrary code—a technique known as Remote Code Execution (RCE). Because PHP typically executes with elevated system permissions, an exploit of this nature can allow malicious actors to read private user databases, intercept sensitive credentials, deploy malware, or deface websites entirely.
Crucially, because these flaws reside in the foundational code of PHP itself, they bypass standard application-level protections, such as web application firewalls (WAFs) and login authentication checks, leaving even otherwise well-secured websites vulnerable.

Chronology of Events
The timeline surrounding the discovery, evaluation, and public disclosure of these vulnerabilities underscores the immense complexity inherent in maintaining open-source software projects.
- 2024 (Initial Discovery): According to statements released by the PHP Foundation, the first of the two serious memory-handling flaws was uncovered during an internal security review and code audit.
- 2024–2026 (Remediation and Delays): Fixing deep architectural bugs within a mature, complex codebase is rarely straightforward. The PHP Foundation acknowledged that the remediation process encountered significant delays due to the intricate nature of the memory management systems involved. Developers had to ensure that any prospective patches did not inadvertently break backward compatibility or destabilize existing applications.
- October 21, 2026 (Public Disclosure and Patch Release): The PHP team officially disclosed both vulnerabilities to the global developer community. Accompanying the disclosure were critical security patches designed to rectify the memory corruption vectors.
- Present Day (The Update Cycle): Website administrators, managed hosting providers, and enterprise IT departments are currently engaged in a massive global race to audit infrastructure, deploy the updated PHP binaries, and scan for potential indicators of prior compromise.
Security analysts emphasize a vital distinction: the fact that the first bug was discovered in 2024 does not automatically imply that malicious hackers were actively exploiting it for two full years. Discovering a vulnerability, developing a reliable exploit proof-of-concept, responsibly reporting the issue, and observing active exploitation in the wild are entirely separate phases of the cybersecurity lifecycle.
Supporting Data and The Scale of Impact
To understand the gravity of the October 2026 PHP disclosure, one must examine the sheer volume of digital architecture reliant on the language. PHP (a recursive acronym for PHP: Hypertext Preprocessor) powers a staggering percentage of the dynamic web.
While exact metrics fluctuate, industry data consistently demonstrates that PHP underpins upwards of 70% to 75% of all websites with known server-side programming languages. This includes:
- Content Management Systems (CMS): Platforms like WordPress, Drupal, and Joomla—which collectively manage nearly half of all active websites on the internet—rely heavily on PHP.
- E-Commerce Ecosystems: Major online shopping platforms and modular e-commerce plugins use PHP to process transactions, manage customer inventories, and interface with payment gateways.
- Enterprise and Institutional Portals: Countless corporate intranets, news publications, and membership portals use custom or framework-based PHP scripts (such as Laravel or Symfony) to manage user sessions and database queries.
The economic and operational footprint of this vulnerability is vast. Unlike localized software bugs that affect a single application, a core language flaw impacts systems across every tier of hosting:

- Shared Hosting Environments: Low-cost, multi-tenant hosting providers often house thousands of independent websites on a single physical server. If the host environment’s PHP installation is unpatched, a compromise of one site can potentially cascade across neighboring directories.
- Enterprise Infrastructure: Large organizations rarely run a single instance of PHP. Enterprise networks often feature distributed architectures with live production servers, internal staging environments, legacy microservices, and continuous integration (CI/CD) pipelines—all of which must be individually identified, updated, and verified.
Official Responses and Industry Reactions
The PHP Foundation, alongside independent cybersecurity firms and major Linux distributions, mobilized immediately following the October 21 disclosure.
In statements released alongside the patches, the PHP Foundation addressed the timeline of the disclosure, admitting that the prolonged gap between the initial 2024 discovery and the 2026 patch release highlighted structural challenges within open-source maintenance. Maintaining widely used foundational software often relies on volunteer contributions, underfunded audits, and complex coordination across diverse operating system maintainers.
Prominent software vendors and hosting providers echoed these sentiments, releasing emergency advisories urging system administrators to apply the patches immediately. Major Linux distributions—including Ubuntu, Red Hat, Debian, and Amazon Linux—pushed out updated PHP packages to their respective repositories within hours of the public announcement.
Cybersecurity agencies worldwide have reinforced these calls to action, noting that automated scanning scripts deployed by malicious botnets typically target newly disclosed vulnerabilities within 48 to 72 hours of public disclosure. Consequently, organizations failing to update promptly face an exponentially rising risk of automated intrusion.
Implications and Next Steps for the Digital Ecosystem
The exposure of these core PHP vulnerabilities serves as a stark reminder of the fragile interconnectedness of the modern internet. It highlights several broader realities regarding digital security:

1. The Limits of Defense-in-Depth
A secure website is not a monolithic structure; it is a stack of interdependent layers. As security experts point out, robust encryption protocols (such as HTTPS/TLS) ensure data privacy in transit, and strong passwords protect user accounts. However, neither measure can neutralize a flaw residing deep within the server’s execution engine. If the underlying language code can be manipulated, peripheral security controls can be bypassed entirely.
2. The Operational Burden of Patching
For website owners and system administrators, downloading a patch is only the first step. The remediation process requires a disciplined, multi-stage approach:
- Asset Discovery: Organizations must catalog every instance where PHP is installed—including forgotten staging sites, internal testing servers, and legacy applications.
- Deployment and Testing: Patches must be applied and rigorously tested to ensure that updated libraries do not disrupt custom codebases or third-party plugins.
- Forensic Auditing: Because the vulnerabilities allow remote code execution, simply applying a patch is insufficient if a server was already compromised prior to the update. Administrators must inspect server logs, check for unauthorized file modifications, reset compromised credentials, and—in severe cases—rebuild affected environments from scratch.
3. Responsibilities Across the Stack
- For End Users: Casual web visitors do not need to take any direct action. The responsibility for securing infrastructure rests entirely with website operators, developers, and hosting providers.
- For Website Owners (Managed Hosting): Individuals utilizing managed hosting platforms should proactively contact their service providers to confirm that the server’s PHP environment has been updated to the latest secure version.
- For System Administrators and Developers: Those managing dedicated servers must perform comprehensive audits, update all PHP runtimes across all environments, and monitor security advisories for potential secondary exploits.
Ultimately, the October 2026 PHP security incident underscores a quiet truth of the digital age: the vast majority of the internet runs on foundational tools that operate silently in the background. When those foundations experience tremors, securing the digital ecosystem requires coordinated, deliberate effort from developers, maintainers, and administrators alike.